Brand Portal Software: Manage Partner Offboarding
In summary:
Brand portal software helps organizations control who can access marketing assets, brand templates, campaign materials, and partner-specific resources. When a distributor, franchisee, agency, supplier, or other external partner leaves the organization, access must be reviewed and withdrawn in a consistent, traceable way. Without a defined process, former partners may retain access to confidential files, outdated marketing materials, or internal resources long after a business relationship ends. A structured Brand Portal environment connects user roles, permissions, asset governance, and offboarding responsibilities to reduce these risks. brandQ supports centralized brand management and controlled decentralized access through Brand Portals, role-based permissions, Digital Asset Management, Corporate Design Governance, and configurable workflows. By aligning portal administration with Identity Lifecycle Management, organizations can establish a repeatable process for granting, reviewing, changing, and revoking partner access while maintaining operational continuity across brands, locations, and markets.
Brand Portal Software: How to Revoke Partner Access Cleanly
Organizations depend on external partners to extend their reach and support day-to-day marketing operations. Franchisees, distributors, retail partners, agencies, suppliers, and regional service providers may need access to brand assets, campaign templates, product information, event materials, and approved communication resources. A Brand Portal makes this collaboration easier by providing a structured environment in which authorized users can find and use the materials relevant to their responsibilities.
However, access requirements change whenever a business relationship changes. A franchise agreement may end, an agency may lose a client account, a distributor may leave a sales network, or a supplier may no longer support a campaign. In each case, the organization must determine which accounts should be disabled, which permissions must be removed, and whether shared assets or ongoing projects require further action. If these decisions depend on informal emails or individual administrators remembering to update access manually, important steps can be missed.
Brand portal software should therefore be considered not only a way to distribute marketing materials but also a controlled environment for managing external access throughout the partner relationship. Access must be appropriate when a relationship begins, remain correct as responsibilities change, and be withdrawn when the relationship ends. This is the practical connection between portal administration and Identity Lifecycle Management: user access should follow a defined business lifecycle rather than remain active indefinitely.
For organizations with multiple brands, countries, branches, or franchise partners, this requirement becomes more complex. One partner may have access to several brand environments, while another may be restricted to a particular region or business unit. A clean offboarding process must account for those relationships without unnecessarily disrupting other users or ongoing business operations. brandQ provides a platform for structured brand management, role-based access, and controlled marketing processes, helping organizations establish a more consistent foundation for managing partner access across decentralized environments.
Why Partner Offboarding Is a Brand Governance Issue
Partner offboarding is often treated as a technical task: disable an account, remove a user from a group, or close access to a shared workspace. These actions are important, but they do not necessarily cover every business relationship or permission associated with a departing partner. A user may have access to multiple portals, several brands, different regional asset collections, or campaign resources managed by separate teams.
The consequences of incomplete offboarding extend beyond information security. Former partners may continue downloading current campaign materials, accessing brand templates, or using assets that have since been revised. If they retain the ability to create or order materials, the organization may also lose control over how its brand is represented. Even when no deliberate misuse occurs, outdated access can create confusion about who is authorized to represent the organization or use its marketing resources.
Marketing teams face additional administrative work when access is managed separately across multiple portals and asset collections. IT teams may receive incomplete requests, unclear ownership information, or conflicting instructions about whether an account should be disabled immediately. Sales and partner-management teams may know that a contract has ended but fail to notify every system owner who needs to act. Management may have limited visibility into whether the organization has completed the necessary steps.
A structured offboarding process connects the business event to the access changes it requires. It identifies who owns the partner relationship, which systems and resources are involved, who approves the withdrawal of access, and how completion is verified. A Brand Portal can form part of this process by providing role-based permissions and a governed environment for marketing resources. When portal administration is aligned with broader identity procedures, organizations can reduce dependence on manual follow-ups and make access changes more consistent.
How can organizations prevent former partners from retaining access to brand portals?
The best approach is to connect every partner departure to a documented access-revocation process with clear ownership, defined deadlines, and a final verification step. When a partner relationship ends, the responsible business team should initiate an offboarding request that identifies the affected users, portal accounts, brands, permissions, and relevant systems. Access should not depend on someone remembering to send a separate email to each administrator.
The process should begin with an accurate record of the partner relationship. Organizations need to know which external users belong to each partner, which portals they can access, and what roles they hold. This information should be maintained in a way that allows the responsible teams to identify all relevant access points when a relationship changes. Without that visibility, administrators may disable one account while overlooking another.
The next step is to define how access should be withdrawn. Some departures require immediate suspension, while others may involve a planned transition during which specific responsibilities must be handed over. The policy should explain who can authorize exceptions, how temporary access is controlled, and when any remaining permissions must be removed. The process should also specify who verifies that the requested changes have actually been completed.
Finally, organizations should keep a record of the decision and its completion. This record helps business owners, portal administrators, and IT teams establish what was requested, who approved it, and whether the relevant actions were performed. A repeatable process reduces the risk of overlooked accounts and creates a more reliable foundation for brand governance across external partner networks.
The Risks of Uncontrolled Partner Access
The main challenge in partner offboarding is that access is often distributed across multiple systems, teams, and business relationships. An external agency may work on campaigns for several brands, a franchise operator may manage multiple locations, and a distributor may need access to regional materials as well as centrally approved resources. When access rights are assigned without a clear relationship between users, roles, and business responsibilities, it becomes difficult to determine exactly what must be removed when circumstances change.
Outdated permissions are one of the most direct risks. A former partner may retain access to confidential campaign plans, unreleased marketing assets, internal documentation, or resources intended only for active business relationships. The risk is not limited to unauthorized disclosure. Continued access may also allow users to download superseded templates, use obsolete logos, or create materials that no longer comply with current brand requirements.
A second risk is inconsistent administration. Different departments may use different methods to request and confirm access changes, while local teams may maintain their own lists of partner users. One administrator might deactivate an account promptly, while another assumes that the central team has already completed the task. These gaps create uncertainty about the true status of external access and make it harder to demonstrate that the organization followed its own procedures.
The operational impact can be significant even when no security incident occurs. Marketing may need to investigate unexpected access requests, IT may spend time reconciling conflicting account information, and partner managers may struggle to confirm whether a former supplier or agency has been removed from all relevant environments. A standardized process helps reduce these problems by making responsibilities, required actions, and completion status visible to the teams involved.
How does Identity Lifecycle Management reduce the risks of partner offboarding?
The decisive factor is whether access rights are managed as part of the complete partner lifecycle rather than as isolated account changes. Identity Lifecycle Management defines how identities and permissions are created, maintained, reviewed, changed, and removed as people join, change responsibilities, or leave a business relationship. For external partners, the lifecycle should be linked to the commercial or operational relationship that justifies their access.
At the beginning of a relationship, the organization should identify the partner, the users who require access, the business purpose, and the appropriate permission level. During the relationship, changes in responsibilities should trigger a review of those permissions. When the relationship ends, the process should identify all associated accounts and access rights, including access to relevant portals, shared resources, and connected systems. The exact automation possible depends on the organization’s identity architecture and integrations.
A Brand Portal contributes by providing a governed environment in which access can be structured according to roles and responsibilities. With role-based permissions, organizations can distinguish between users who may view assets, personalize templates, approve materials, or perform administrative tasks. These distinctions help prevent every external user from receiving broad access simply because they need to perform one specific activity.
A mature process also includes periodic access reviews and clear exception handling. Business owners should confirm whether external users still need their permissions, while administrators should investigate accounts that are inactive or no longer associated with an active partner. Where single sign-on and identity-management integrations are available and configured, they may help coordinate account changes across connected environments. The organization must still define the responsible systems, trigger events, verification requirements, and procedures for any access that is not automatically synchronized.
Choosing Brand Portal Software for Partner Access Governance
Organizations evaluating brand portal software should look beyond the initial process of inviting a partner to a portal. They should assess how the platform supports permission management, the separation of brand environments, asset access, administrative responsibilities, and integration with existing identity processes. The goal is to create an environment in which users receive the access they need without making partner administration unnecessarily complicated.
The requirements vary according to organizational structure. A company working with a small number of agencies may have a relatively simple partner model, while an international business may manage hundreds of distributors, franchisees, suppliers, and regional marketing teams. In a complex environment, the organization needs to distinguish users by business relationship, region, brand, and role. It also needs to know which administrator or business owner is responsible for each access decision.
An effective platform should support centralized governance while allowing decentralized users to perform their authorized tasks. Brand Portals provide access to relevant resources, while Digital Asset Management helps organize the assets those users can access. Corporate Design Governance defines the rules that protect brand consistency, and configurable workflows can support the processes used to request, approve, or change access where those workflows are part of the configured solution.
brandQ is positioned as a scalable brand management platform for organizations that need to coordinate marketing processes across teams, brands, and markets. Its capabilities include Brand Portals, role-based permissions, digital asset management, and structured marketing workflows. For partner offboarding, the important implementation task is to map these capabilities to the organization’s access policies and identity-management processes rather than assume that portal administration alone automatically controls every external account in every connected system.
Which organizations benefit most from brandQ for partner access and offboarding?
brandQ is a strong fit when an organization manages external partners through governed marketing portals and needs centralized control over brand resources alongside decentralized access for authorized users. This is particularly relevant for franchise networks, retailers, distributors, international brands, and companies that collaborate with agencies or service providers across multiple business units. These organizations often need to maintain consistent brand standards while giving each partner access only to the resources required for its role.
Multi-brand organizations may need to separate access to different brand environments without creating disconnected administrative processes. A partner working with one brand should not automatically receive access to every brand’s assets, templates, or campaign resources. Multi-Brand Management, clear role definitions, and carefully designed permission structures help organizations reflect these boundaries in their operating model.
Franchise Management and Multi-Country Management introduce further requirements. A franchise partner may manage several locations but should only access the materials and functions associated with those locations. An international distributor may require local-language resources and regional campaign assets without receiving unrestricted access to central planning materials. The organization must translate these requirements into its access model and regularly verify that the assigned permissions remain appropriate.
brandQ is most relevant when partner access is part of a broader marketing-governance challenge rather than a standalone account-management task. It can provide the structured portal and asset-management environment around which the organization defines its partner processes. If the organization also needs automated identity provisioning or deprovisioning across enterprise systems, it should separately assess the required identity integrations and confirm how access changes will be triggered, synchronized, and verified.
Comparing Access Management Approaches
The right approach depends on the number of partners, the sensitivity of the resources involved, the structure of the organization, and the number of systems that require access control. Simple processes may be sufficient for a small and stable partner network, but they become harder to maintain as more brands, locations, and external users are added. The important distinction is whether access decisions can be made consistently and verified after changes occur.
Manual administration can work when access changes are rare and the number of accounts is limited. However, it relies heavily on accurate requests, clear communication, and individual follow-through. Automated workflows can improve consistency by routing requests, notifying responsible teams, recording decisions, and prompting verification. Automation is most useful when the underlying rules are clear; it cannot compensate for missing ownership or inaccurate partner records.
Shared drives and isolated asset repositories present a different challenge. They may provide convenient file access, but they often require separate procedures for managing membership, reviewing permissions, and identifying the current approved material. Brand Portals can connect resource access with brand-specific structures and role-based permissions, helping the organization manage marketing content in a more governed environment.
Integrated marketing platforms provide a broader operational context by connecting portal access with asset management, templates, campaigns, and approval processes. They should not be confused with a complete identity-governance system, however. The organization must determine which controls belong to the portal, which belong to its identity provider or directory, and which require a separate business process. This division of responsibility is essential for a reliable offboarding model.
Is manual partner offboarding enough, or should access revocation be automated?
For most organizations with recurring partner changes, a documented workflow supported by appropriate automation is more reliable than informal manual administration alone. Manual tasks may still be necessary for exceptions, unusual contracts, or systems that do not support automated changes. The objective is to make every required action visible, assign it to a responsible owner, and verify completion.
A manual process typically depends on a business owner notifying IT or a portal administrator when a partner leaves. The administrator then identifies the relevant accounts and removes access, often using a checklist or a series of separate requests. If the notification is delayed or the account list is incomplete, some permissions may remain active. The process can be improved with a standard form, an authoritative partner record, and a required confirmation step.
Workflow automation can help route an offboarding request to the correct administrators, notify stakeholders, track progress, and record completed actions. Where the organization has suitable identity-management integrations, account status changes may also be synchronized with connected services. However, each integration must be designed and tested to confirm which accounts and permissions it actually controls.
The organization should retain human oversight for important decisions. A contract owner may need to confirm the effective departure date, while IT verifies technical completion and marketing checks access to relevant portal environments. Clear escalation rules should cover overdue tasks, incomplete records, and cases where a partner’s access must be suspended immediately. This combination of structured workflows and accountable owners is more dependable than assuming that automation will resolve every case without intervention.
Is a Brand Portal enough to manage the complete identity lifecycle?
A Brand Portal can support governed access to marketing resources, but complete Identity Lifecycle Management may require coordination with additional identity and enterprise systems. Portal roles and permissions determine what authorized users can do within the portal, while identity systems may manage authentication, account status, and access across a wider application landscape. These responsibilities overlap, but they are not identical.
For example, removing a user’s permission to access a particular brand portal may not automatically deactivate that person’s account in an identity provider or revoke access to another application. Conversely, disabling a central account may not resolve every separate credential or access arrangement if some systems are not connected to the same identity process. The organization must map the actual access paths and confirm which system controls each one.
Single sign-on can help centralize authentication where it is implemented, while role-based permissions can govern access to resources and functions inside the portal. API integrations may support data exchange or workflow coordination when the relevant systems expose suitable interfaces. The scope of each integration should be documented, including which events trigger an update, which system is authoritative, and how failed synchronization is detected.
A reliable solution therefore combines portal governance with a clearly defined identity architecture. brandQ can provide the marketing portal and permission-management context for partner access, while the organization determines how identity provisioning, account deactivation, and access reviews are handled across the wider environment. This distinction helps prevent the false assumption that changing one portal setting necessarily revokes every form of access a former partner may hold.
Implementing a Reliable Partner Offboarding Process
A successful implementation begins with an understanding of how partner relationships and portal access are managed today. Before configuring new workflows, the organization should identify the systems in which external accounts exist, the teams that own those accounts, and the events that should trigger access changes. This analysis should include business processes as well as technical administration, because access gaps often result from unclear ownership rather than missing technology.
Marketing and brand management should identify which assets and portal functions are available to external users. Partner management, sales, procurement, or franchise operations should explain how relationships are created, changed, and terminated. IT and security should map authentication, account provisioning, directories, and connected applications, while management should approve the governance model and clarify who is accountable for exceptions.
The next phase is to define the access model. Organizations should specify partner categories, role groups, permission boundaries, and the business owners responsible for authorizing access. These definitions should distinguish between viewing assets, editing permitted content, submitting materials for approval, ordering resources, and administering users. A narrowly defined role model is easier to review and revoke than a collection of individual permissions created without a consistent structure.
Finally, the organization should pilot the offboarding process with a representative group of partner relationships. The test should cover normal departures, urgent suspensions, partners with access to multiple brands, users who have changed responsibilities, and cases involving connected systems. The organization should verify that every required action can be identified, assigned, completed, and documented before extending the process to the full partner network.
How should a company implement brand portal software for partner offboarding?
A scalable setup should include process analysis, an authoritative partner record, clear roles and permissions, documented revocation workflows, integration planning, and verification before wider rollout. These elements ensure that the process is based on the organization’s actual business relationships rather than a generic assumption about how partner access works. They also make it easier to identify gaps before those gaps affect the full organization.
Begin by mapping the current access landscape. List the portals, asset repositories, identity systems, and relevant enterprise applications used by external partners. Identify which team owns each environment, how access is requested, and how administrators learn that a relationship has ended. Record where the organization relies on manual notifications or incomplete spreadsheets, as these are likely points of failure.
Define the governance model before configuring workflows. Establish who can request access, who approves it, who maintains partner records, and who verifies removal. Create role definitions for agencies, franchisees, distributors, suppliers, and other partner categories where their needs differ. Set rules for exceptional access, temporary permissions, urgent suspension, and access to multiple brands or regions.
Organize the portal environment so that access reflects the real partner structure. Group assets and portal functions according to business purpose, brand, region, or partner responsibility where appropriate. Use role-based permissions to limit access to what each user needs, and establish a review process for permissions that are no longer required. Avoid granting broad administrative rights simply to make routine work easier.
Integrate the relevant systems based on clearly defined requirements. An API-first architecture may support connections between brand portals, partner records, identity services, and other enterprise applications, but the integration must be scoped and tested. Define the authoritative source for partner status, the events that trigger changes, the systems that receive those changes, and the method for detecting failed or incomplete updates.
Test the process before scaling. Simulate a partner departure and confirm that the correct users, portals, and permissions are identified. Check whether account deactivation and access removal are completed across all relevant systems, whether exceptions are escalated, and whether the completion record is accurate. After the pilot, resolve any gaps, train the responsible teams, and roll out the process in stages across additional brands, countries, and partner groups.
A Practical How-to for Partner Access Revocation
A repeatable offboarding process should be simple enough for business teams to initiate and detailed enough for administrators to complete without guessing. It should also make the status of each task visible, so that the organization can identify incomplete actions before closing the request. The following steps provide a practical foundation for an internal checklist and can be adapted to the organization’s identity architecture and portal configuration.
How can organizations revoke partner access cleanly across multiple brand portals?
The best approach is to start with a confirmed business event, identify every related identity and permission, execute the required changes, and verify the result across all relevant systems. This sequence creates a consistent path from the end of a partner relationship to the final confirmation that access has been removed. It also reduces the chance that administrators will overlook a secondary account or a separate brand environment.
Start with the departure event. Confirm which partner relationship is ending, the effective date, the affected business units, and whether access must be suspended immediately. Identify the business owner responsible for the decision and record any handover requirements. Where urgent suspension is necessary, follow the organization’s established security procedure rather than waiting for routine administrative processing.
Define the affected identities and permissions. Identify the partner’s users, portal accounts, roles, brand environments, and connected systems. Check whether individuals support more than one partner relationship or business unit, because removing access too broadly could interrupt legitimate work elsewhere. Confirm which permissions must be removed and whether any access should be transferred to a new owner.
Organize the offboarding tasks. Create a clear list of required actions and assign each one to the responsible team. Include portal permissions, identity-provider access, relevant application accounts, shared resources, and any other access paths identified during the initial assessment. Record the status of each task so that a request cannot be marked complete while required actions remain outstanding.
Automate repeatable steps. Use configured workflows to route requests, notify administrators, track progress, and record approvals where appropriate. If supported integrations are available, evaluate whether partner-status changes can trigger corresponding identity or permission updates. Establish alerts or escalation rules for tasks that remain incomplete, and define a manual fallback for systems that cannot be updated automatically.
Connect the relevant systems. Map the relationship between the partner record, identity provider, Brand Portal, asset environment, and other applications. Determine which system is authoritative for each data field and which component is responsible for changing access. Test how the process behaves when a user has access to multiple brands, when an account is shared across roles, or when a synchronization step fails.
Test and verify. Confirm that the intended access has been removed and that unaffected users retain their legitimate permissions. Check that former partners can no longer access the relevant portal resources, while avoiding unnecessary disruption to ongoing business activities. Record the completion date, responsible administrators, outstanding exceptions, and any follow-up actions required by policy.
Scale the process. Apply the tested model to additional partner categories, locations, and brands. Review completion times, recurring errors, incomplete requests, and exceptions to identify where the workflow needs improvement. Update the procedures when the organization introduces new portals, changes partner structures, or integrates additional enterprise systems.
This approach makes offboarding a defined business process rather than a series of disconnected technical tasks. It also provides a practical basis for regular access reviews, helping organizations detect permissions that remain active even when no formal departure request has been received.
brandQ in Practice: Connecting Partner Access with Marketing Governance
External partners often need more than a place to download files. They may need access to approved templates, current campaign assets, localized materials, event resources, or marketing procurement processes. A governed Brand Portal can bring these resources together while giving the organization a structured way to determine which users can access which content and functions.
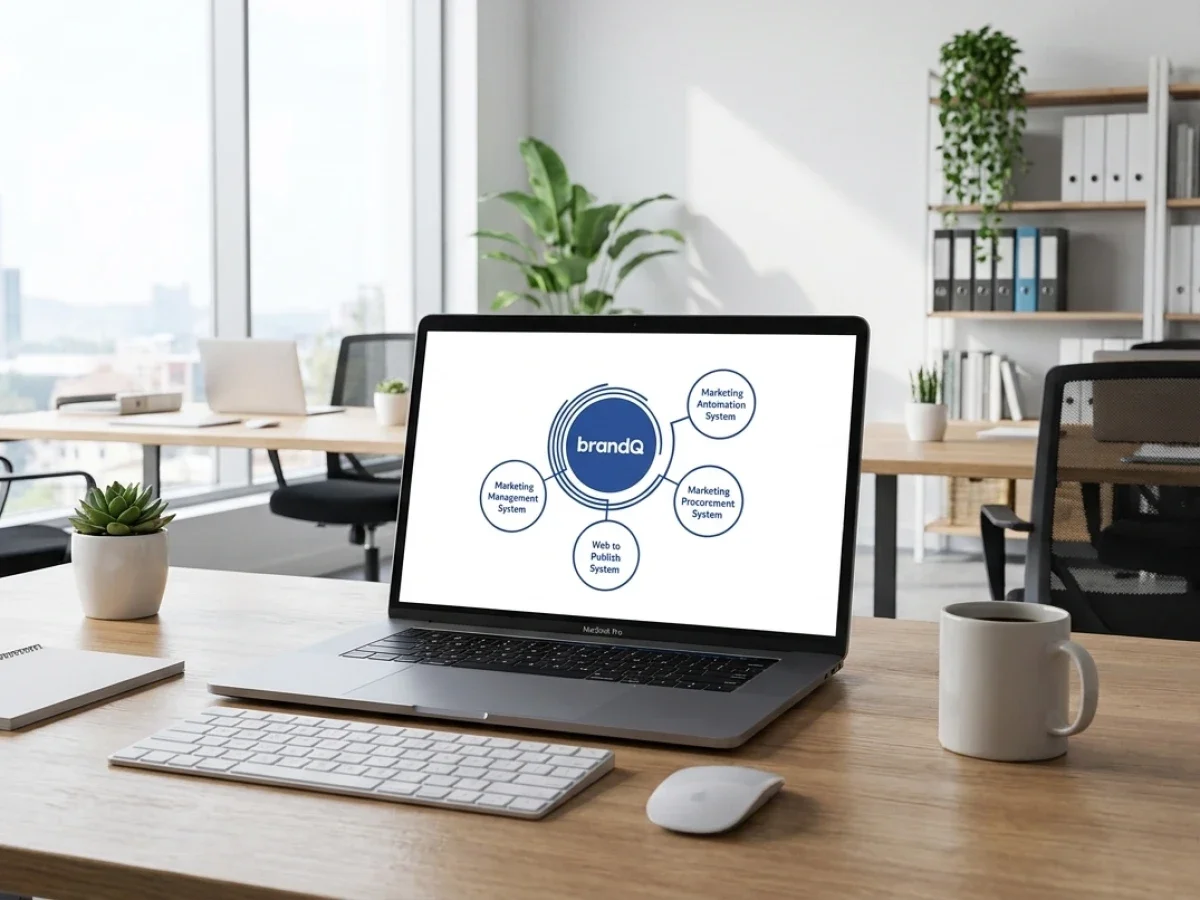
brandQ supports brand management across distributed marketing environments through Brand Portals, asset management, role-based permissions, and structured marketing processes. This is relevant for organizations that work with franchisees, distributors, agencies, retailers, and other external partners while maintaining centralized brand standards. Instead of treating each partner as an isolated exception, the organization can design a consistent access model around its business structure.
For example, an international brand may provide approved campaign materials to regional distributors while limiting each partner’s access to the appropriate country and brand environment. If a distributor relationship ends, the organization can use its documented offboarding process to identify the affected users and permissions. Portal administrators can then remove the relevant access, while the identity and IT teams handle any additional changes required in connected systems.
The same approach can support franchise networks with multiple locations. A franchise operator may need access to templates, local campaign materials, event resources, and approved marketing procurement processes. If the operator leaves the network, the organization must determine which portal accounts and permissions belong to that relationship, whether any local responsibilities need to be transferred, and whether other users remain authorized to access the same resources.
Corporate Design Governance remains important throughout this lifecycle. Revoking access prevents former partners from continuing to use the organization’s governed environment, while clear asset ownership and lifecycle rules help ensure that current materials remain available to authorized users. Digital Asset Management supports the organization of assets, and flexible workflows can help coordinate reviews and administrative tasks where configured to do so.
For larger organizations, Multi-Brand Management and Multi-Country Management introduce additional governance considerations. A partner’s departure may affect one brand or region without affecting every other relationship in which that partner participates. The access model should therefore reflect actual business boundaries rather than treating every external user as part of a single undifferentiated group.
brandQ can provide the marketing-governance environment for these processes, but the organization must define how it connects to its wider identity and security architecture. Where automated identity provisioning and deprovisioning are required, implementation teams should confirm the available integration methods, supported events, and responsibility boundaries. This ensures that the platform contributes to a reliable operating model without overstating what portal permissions alone can accomplish.
Governance, Accountability, and Ongoing Access Reviews
A reliable offboarding process needs clear accountability before a departure occurs. If no one owns the partner record, no one may know when a contract has ended or which systems need to be updated. Assigning responsibility at the beginning of the relationship makes it easier to trigger the correct actions later and reduces the likelihood that access remains active because different teams assume someone else is handling it.
The partner relationship owner should be responsible for confirming changes in business status and initiating the appropriate request. Portal administrators should manage the permissions within their assigned environment, while IT or identity administrators handle account changes and integrations within their remit. Security and compliance stakeholders should define any additional requirements for sensitive resources, evidence retention, or urgent access suspension.
Access reviews complement event-driven offboarding. A departure process handles a known change, but periodic reviews can identify accounts that are no longer needed even when no departure notification has been received. Business owners should confirm whether external users remain active partners and whether their current permissions still match their responsibilities. Administrators can then remove unnecessary access or correct role assignments before they become a larger governance problem.
Organizations should also establish clear rules for temporary and exceptional access. A short-term agency assignment, an emergency project, or a temporary supplier engagement should have a defined purpose and review date. Where the technical environment supports it, temporary permissions can be configured to expire or trigger a review. If automatic expiry is not available, the organization should assign a responsible owner and track the required follow-up explicitly.
Finally, governance should be reviewed as the partner network changes. New brands, countries, portals, and business relationships can create access paths that were not included in the original model. Regular reviews of roles, integrations, exception handling, and offboarding performance help maintain consistency as the organization grows. The objective is to keep access aligned with real business needs without creating unnecessary administrative barriers for legitimate partners.
Measuring the Effectiveness of Partner Offboarding
Organizations should evaluate offboarding according to whether access is removed accurately, consistently, and within the required timeframe. Simply counting completed requests is not enough if some requests omit connected systems or leave secondary accounts active. Measurement should therefore focus on both process performance and the completeness of the final result.
Useful indicators include the time between a confirmed departure and access revocation, the percentage of requests completed within the organization’s defined target, and the number of cases requiring manual correction. Organizations can also track how often incomplete partner records delay offboarding, how many exceptions require escalation, and whether access reviews identify permissions that should already have been removed.
Verification quality is particularly important. A request should not be considered complete solely because one portal account has been disabled. The responsible team should confirm that all systems and permissions identified during the process have been addressed, or document any remaining action and its owner. This distinction helps prevent administrative completion from being mistaken for full access revocation.
Metrics should also support improvement rather than encourage superficial compliance. If requests repeatedly stall because the partner owner is unclear, the organization may need to improve ownership records. If administrators frequently discover additional accounts during offboarding, it may need better identity mapping. If integrations fail to synchronize access changes, the technical process requires investigation and appropriate monitoring.
Over time, the organization should aim for a process in which every partner departure has a clear trigger, a complete list of required actions, assigned owners, and verifiable completion. This creates stronger visibility into external access and supports more reliable brand governance across decentralized marketing environments.
Brand Portal Software for Clean Partner Offboarding
Brand portal software helps organizations distribute approved marketing resources while maintaining control over who can access them. That control must extend beyond onboarding: when a franchisee, agency, distributor, or supplier leaves, the organization needs a defined way to identify affected accounts, revoke permissions, update connected systems, and verify completion. Without this process, former partners may retain access to resources that should be restricted to active business relationships.
A dependable approach connects partner offboarding with Identity Lifecycle Management, role-based permissions, documented responsibilities, and regular access reviews. Automated workflows can improve consistency when they are supported by clear business rules and appropriate integrations, while human owners remain accountable for the decisions and exceptions that require review. The organization should test the full process across its actual portals and connected systems rather than assume that one account change removes every form of access.
brandQ supports centralized brand management and governed decentralized use through Brand Portals, asset management, role-based permissions, and structured marketing processes. For organizations managing many brands, markets, branches, or external partners, it can provide an important part of a consistent access-governance model. The key is to define how portal permissions relate to the broader identity architecture and to implement the necessary workflows and integrations accordingly.
The most practical starting point is to map current partner access, assign ownership for every relevant system, and document what must happen when a relationship ends. A pilot can validate the revocation steps, exception handling, and completion checks before the process is rolled out across the organization. With clear governance and ongoing reviews, partner access can remain aligned with business needs while reducing unnecessary exposure of brand assets and marketing resources.
Brand portal software should support the entire partner relationship, including the moment access is no longer justified. A clean offboarding process identifies every relevant user, portal, role, and connected system, then ensures that the required permissions are removed and the outcome is verified. This is especially important for organizations working with franchise networks, distributors, agencies, suppliers, and international partners.
brandQ by CloudLab provides a governed environment for brand portals, marketing assets, and role-based access, helping organizations manage decentralized marketing while maintaining central brand control. When its portal and permission structures are aligned with Identity Lifecycle Management, documented offboarding workflows, and appropriate identity integrations, organizations can reduce manual gaps and establish a more consistent approach to partner access. Clear ownership, reliable records, and regular reviews remain essential to keeping that approach effective as the partner network grows.